Secure PowerShell Automation Microsoft System Center Orchestrator
The power of PowerShell. The orchestration you trust. Less credential exposure.
With the supplied Azure Key Vault credential provider and correctly configured outputs, target credentials are retrieved at runtime rather than stored in the Orchestrator database or published on its data bus.
Execute a single script or coordinate multiple steps in one remote session, then pass the operational results your runbook needs to subsequent activities.
In addition to the included Azure Key Vault configuration, the integration pack allows you to “bring your own vault” as long as the credential vault has an API you can interrogate via PowerShell.
What is Secure PowerShell?
Secure PowerShell is Kelverion’s integration pack for running Windows PowerShell scripts on remote computers from System Center Orchestrator. It uses PowerShell remoting over Windows Remote Management (WinRM), combining configurable connections with a credential-provider model that separates credential retrieval from runbook logic.
It is not a separate PowerShell language or a replacement for Orchestrator. It is a focused extension that makes your PowerShell scripts available as configurable runbook activities, with defined inputs, useful published outputs, and explicit control over remote sessions.
Extend Orchestrator without embedding credentials in your automation
PowerShell provides the flexibility to automate tasks that depend on your own scripts, application modules or environment-specific logic. Orchestrator provides the workflow that connects those tasks to wider IT processes. Kelverion brings the two together with dedicated activities for credential retrieval, remote execution, session management and result publication.
Positioned alongside Kelverion’s wider Orchestrator Integration Pack portfolio, Secure PowerShell is the practical choice when a workflow needs custom PowerShell execution on a remote Windows machine. Keep your orchestration investment, reuse suitable scripts and adopt a consistent approach to connecting, authenticating and returning results. Your scripts still define the task; the integration pack provides the execution framework.
Typical Automation Scenarios
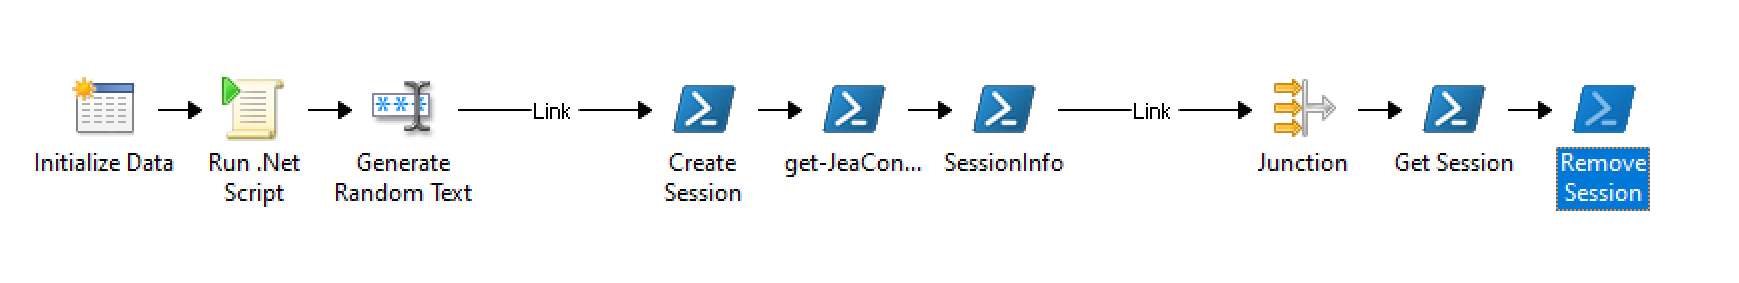
Use Secure PowerShell as the remote execution component within wider Orchestrator workflows.
- Incident diagnostics
Collect service status, running processes, and application health information from a target server, then return selected findings to a service-management workflow - Controlled remediation
Execute an authorized recovery script after the runbook’s required checks or approvals, then validate the outcome and return a clear status - Server and application configuration
Apply environment-specific settings through your existing PowerShell scripts and publish validation results for the next workflow step - Inventory and configuration data collection
Retrieve software versions, server attributes or configuration values for downstream asset or CMDB updates through the appropriate integration - Maintenance validation
Run pre-maintenance checks and post-change verification as part of a broader patching or deployment process - Multi-step administration
Open a remote session, run a sequence of related scripts, collect the required outputs and close the session when the work is complete
Benefits at a Glance
- Reduce credential exposure
Use Azure Key Vault to retrieve target credentials at runtime, keeping them out of the Orchestrator database and databus memory - Bring your own vault
In addition to the included Azure Key Vault configuration, the integration pack allows you to integrate with other credential vaults that have an API you can interrogate via PowerShell - Get more value from existing automation
Bring suitable PowerShell scripts into end-to-end runbooks rather than operating them as disconnected administrative tasks - Reduce repeated connection work
Reuse an open remote session across multiple activities in the same runbook process, avoiding a fresh connection and authentication for every script - Make results easier to use
Map script inputs and outputs to named Orchestrator properties so downstream activities can act on structured operational data - Support consistent runbook design
Reuse connection configurations and script definitions rather than rebuilding connection and parameter-handling logic for each task - Improve troubleshooting context
Pass a Correlation ID into the remote session to help associate script execution with the originating runbook job
Key Capabilities
- External credential retrieval
The supplied Azure Key Vault provider retrieves username and password secrets using the Azure Arc-enabled Runbook Server’s system-assigned managed identity. A custom credential-provider script can support another credential source, provided it follows the documented provider contract - Single-step remote execution
Run Script opens a connection, executes a script, and closes the connection within one activity - Reusable remote sessions
Create Session, Get Session, Run Session Script, and Remove Session provide explicit session lifecycle management for multi-step workflows - Configurable script interfaces
JSON configuration maps activity inputs to script parameters and selected script outputs to published data. Supported options include typed parameters, required inputs, and fixed-value dropdown lists - Inline or file-based scripts
Run script content supplied in an activity or use a script file referenced by its configured ScriptPath - Configurable remoting connections
Set authentication, session endpoint, port, and connection timeouts. The integration pack defaults to HTTPS on port 5986, with certificate-validation checks enabled - Structured results
Publish defined output properties, including multiple records from returned object collections. When no output mappings are defined, activities can return JSON and text representations of script results
Integration Activities
| Activity Name | Description |
|---|---|
| Create Session | Used in a runbook to open a remote PowerShell session to the specified target computer. The session will remain open for later use by the Run Session Script and Get Session activities. When all session work is complete, use the Remove Session activity to close and clean up the session. |
| Get-Session | Used in a runbook to retrieve an existing session by its Session ID |
| Remove-Session | Used in a runbook to close an existing session and release the underlying PowerShell remoting connection to the target computer |
| Run-Script | Used in a runbook to open a remote PowerShell connection to a target computer, run a script, and then close the connection, all in a single activity. The remote session is closed when the activity is completed, and there is no session information stored in the runbook process memory. |
| Run-Session-Script | Used in a runbook to run a script in a session previously opened with Create Session, without opening a new connection |